Beginner
Featured
Cyber Security
Cyber Security Fundamentals
SOC fundamentals, threat modeling, network defence and hardening - your entry point into a high-demand securit...
Defend organisations with SIEM, threat hunting, log analysis, malware triage and incident response inside a simulated SOC.
Defend organisations with SIEM, threat hunting, log analysis, malware triage and incident response inside a simulated SOC.
The SOC Analyst & Blue Team Operations program at ITA Academia is a 12-week, mentor-led track designed around real industry workflows. Every module combines live instruction with guided labs, and ends with a graded deliverable that goes straight into your portfolio.
Graduates receive an ITA Academia verified certificate of completion and a transcript of assessed projects. Selected students are recommended to hiring partners and internship programs.
Basic programming or domain knowledge is recommended. A short readiness quiz is provided during admission.
Hands-on sessions, guided labs and a graded assignment covering soc structure & roles.
Hands-on sessions, guided labs and a graded assignment covering log sources & siem.
Hands-on sessions, guided labs and a graded assignment covering threat intelligence & att&ck.
Hands-on sessions, guided labs and a graded assignment covering alert triage & investigation.
Hands-on sessions, guided labs and a graded assignment covering endpoint detection & response.
Hands-on sessions, guided labs and a graded assignment covering malware triage.
Hands-on sessions, guided labs and a graded assignment covering incident response simulation.
OSCP-certified security engineer who has run red-team engagements and built SOC playbooks for regulated organisations.
SOC fundamentals, threat modeling, network defence and hardening - your entry point into a high-demand securit...
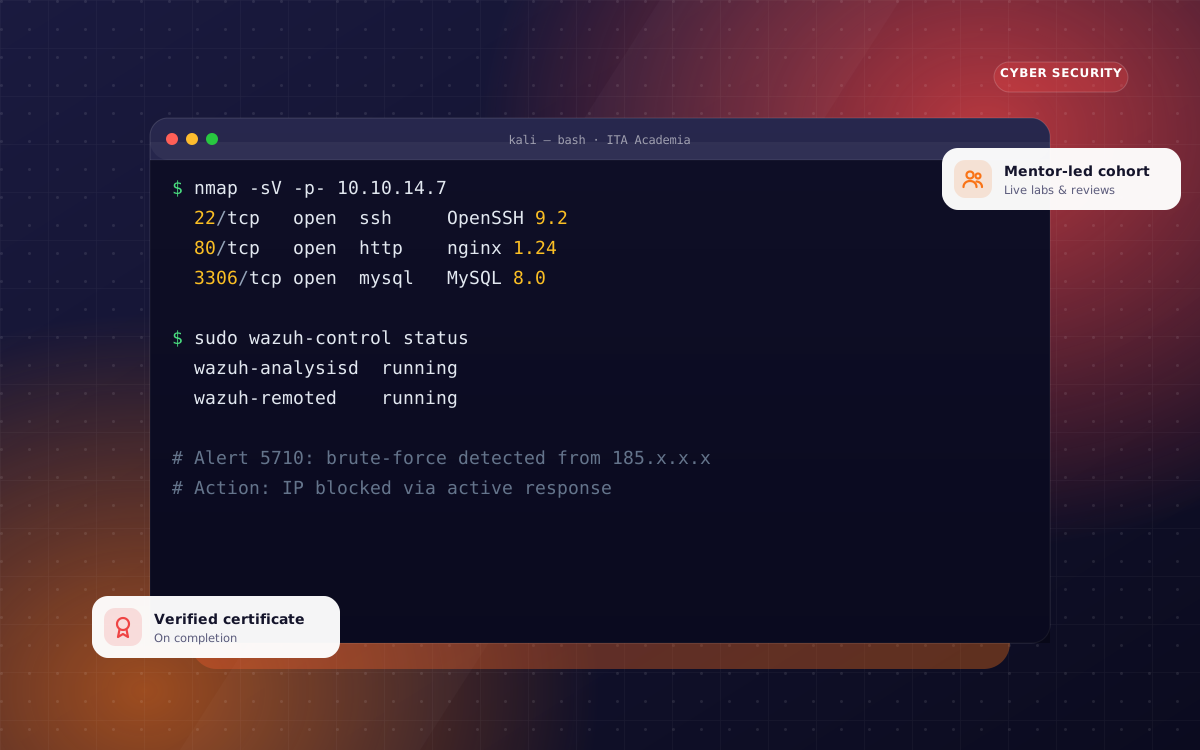
Offensive security with Kali Linux: reconnaissance, exploitation, web app testing, privilege escalation and pr...